About
Understanding From 25+ Years as a Cybersecurity and GRC Executive
Data Defenders is a boutique cybersecurity and AI governance practice built on one person's diagnostic vocabulary — sharpened over 25+ years in the field, 19 of them as a CISO or BISO across six industries, and six as a Managing Director evaluating the security and GRC programs of organizations across nearly every vertical. That perspective is now encoded in the assessment platform.
Founder
Founder and Managing Director. Before Data Defenders, David spent 19 years as a CISO or BISO across payments, government, semiconductor, high-tech, healthcare, and financial services — and six years as a Managing Director evaluating the security and GRC programs of organizations at every scale.
Most security leaders have depth in one or two sectors. That cross-sector diagnostic perspective — knowing what "good" looks like in six different regulatory contexts — is what makes the assessments defensible.
He is a frequent speaker and author on cybersecurity, AI governance, and GRC — and writes the No Hallucinations blog on AI risk and enforcement.
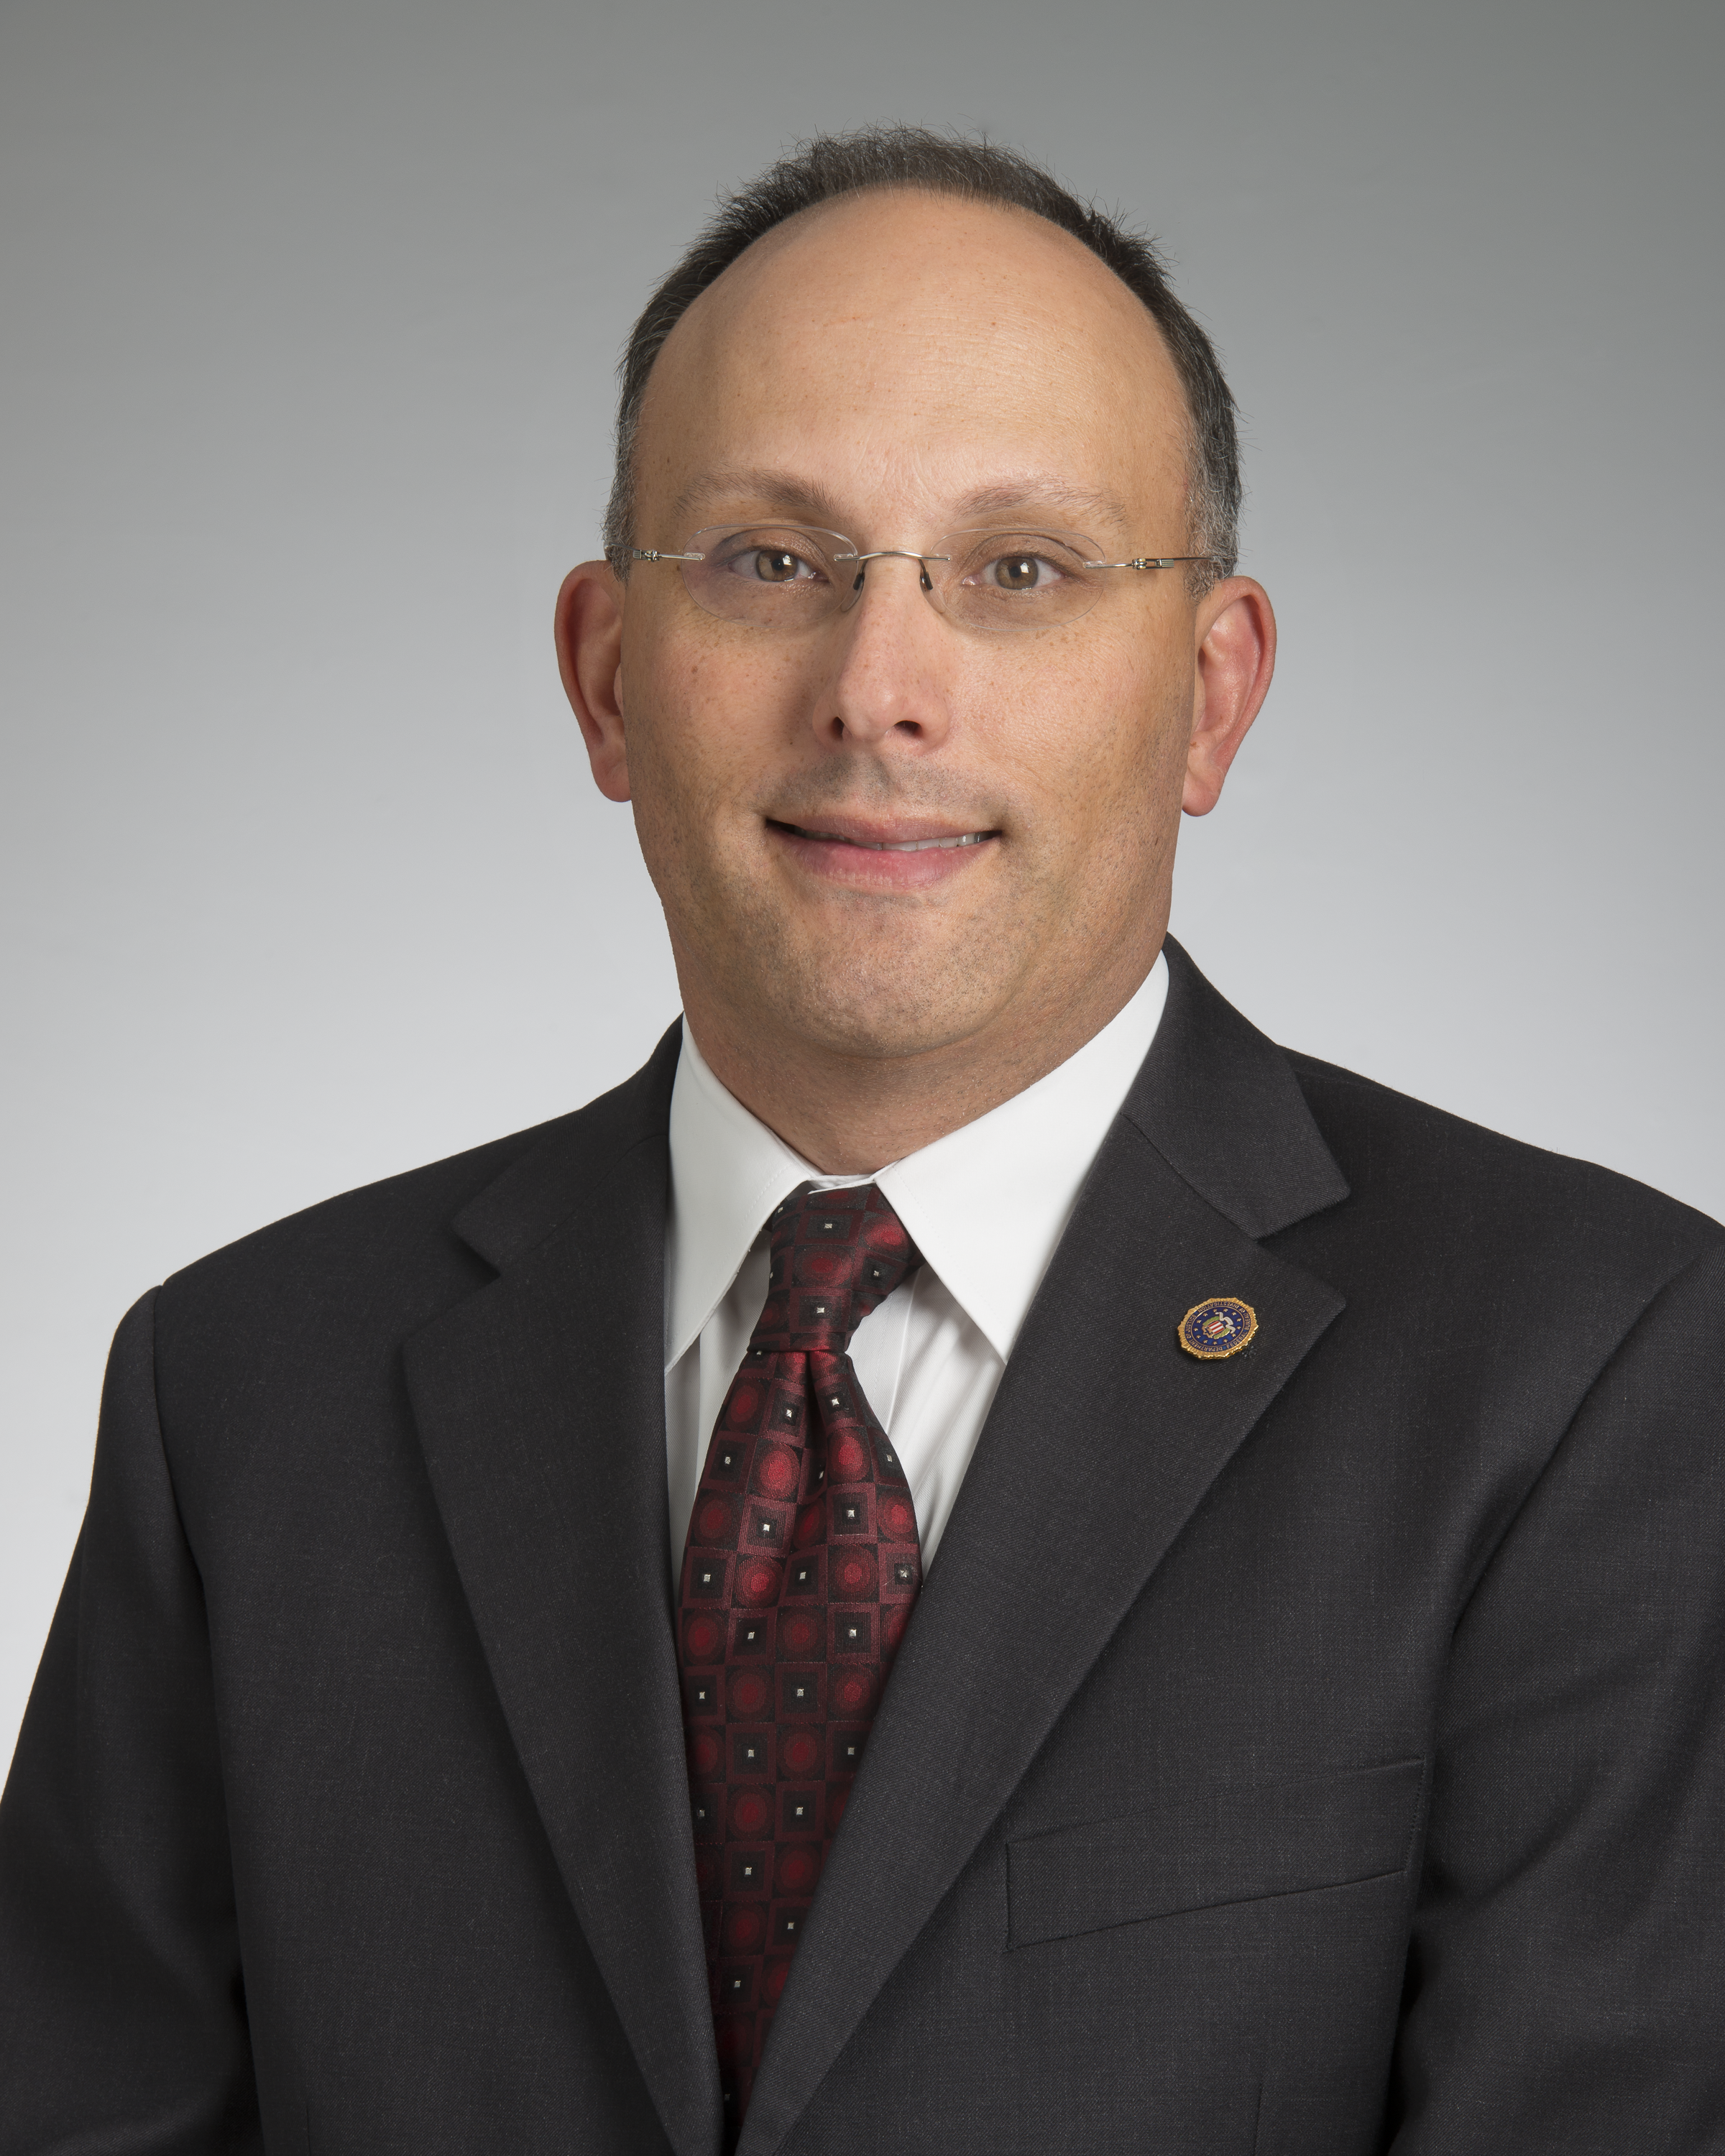
Payments · Gov · Semiconductor · High-Tech · Healthcare · Finance
What we believe
Auditable, Not Advisory
Framework, not opinion
Every question maps to a named control in a recognized standard. Findings cite the control they came from. Nothing invented, nothing proprietary — nothing your auditor can't verify.
Priced, not scoped
Assessment prices are published and fixed by tier. No scoping call to find out what something costs. No hourly meters. The buyer decides on the merits.
Repeatable, not one-off
A versioned compendium lets you re-run the same assessment against updated frameworks. Governance as a trend, not a snapshot.
Talk to Us Directly
Twenty-five minutes. Bring your questions.